NFC identity verification lets a customer prove who they are remotely by reading the chip in their national ID card or biometric passport with their own smartphone. 360 Soft integrates this flow into your mobile app or web onboarding journey and combines it with document, face and liveness checks to build end-to-end remote customer onboarding (e-KYC). Below you will find how NFC-based verification works technically, which organisations need it, the regulatory framework for remote identification, the modules and integration options, implementation steps, the KPIs worth measuring and the main risks. It complements our KYC/AML compliance software overview.
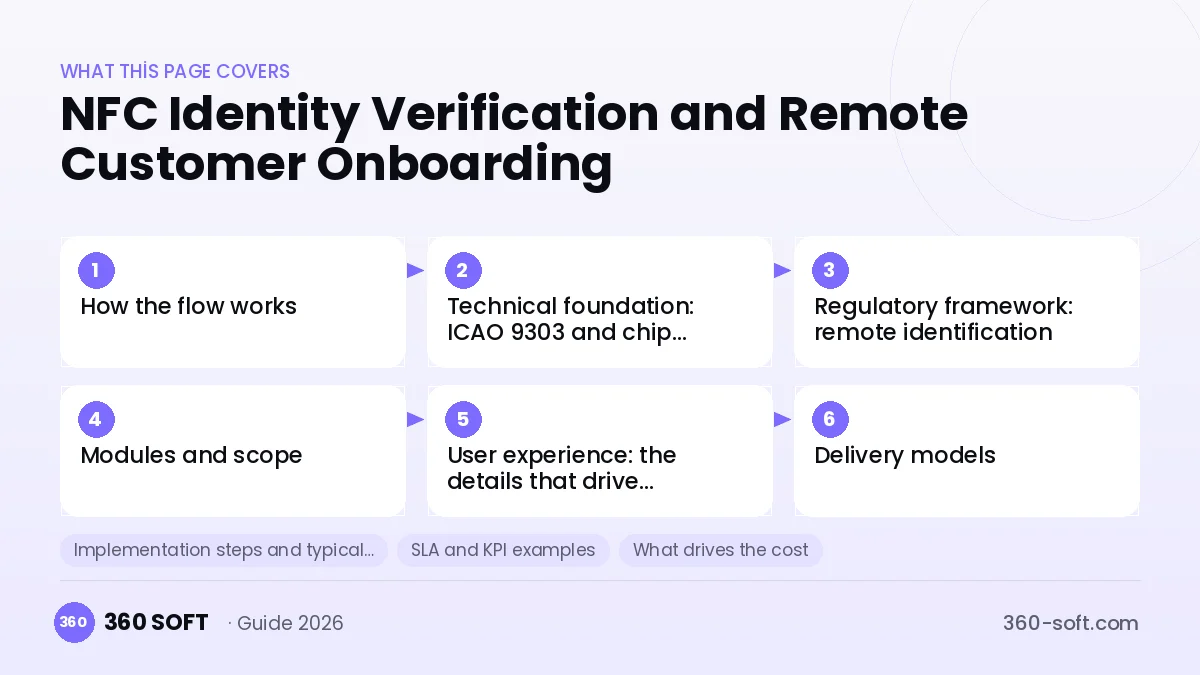
How the flow works
- The customer scans the machine-readable zone (MRZ) or the card access number (CAN) with the camera; this data is used to derive the key that unlocks the chip.
- The card is held against the back of the phone; the app opens a secure channel and reads the personal data and the facial image stored on the chip.
- The signature of the chip data is validated against the issuing state’s certificate chain, proving that the data has not been altered and the chip has not been cloned.
- Liveness detection and face matching confirm that the person in front of the camera is the owner of the chip photo.
- The result is passed to risk scoring and to the compliance team’s dashboard; where required, the case moves on to a video-call step.
- Once approved, the account or contract process starts, and every step is stored in an audit trail.
Technical foundation: ICAO 9303 and chip security
Chip-based national ID cards and biometric passports carry contactless chips that follow ICAO 9303, the International Civil Aviation Organization standard for machine-readable travel documents. Access to the chip requires a key derived from data printed on the document: the older Basic Access Control (BAC) uses the document number, date of birth and expiry date from the MRZ, while the stronger PACE protocol works with the MRZ or the card access number. The chip therefore cannot be read without physical access to the card.
Passive Authentication checks the digital signature over the data groups against the Document Signer certificate and the issuing country’s CSCA root certificate. It proves the data is genuine and unchanged. Active Authentication or Chip Authentication goes one step further: the chip answers a cryptographic challenge with a private key that cannot be extracted, which proves the chip itself is not a copy. A robust solution uses both, and keeps certificate lists (CSCA masterlists and revocation lists) up to date on the server side rather than trusting the device.
Where it is used
- Banks, digital banks and neobanks opening accounts remotely
- Payment and e-money institutions, wallets and remittance apps
- Brokerages, investment platforms and crypto-asset service providers
- Insurance, telecom (SIM registration) and car-sharing or rental platforms
- Marketplaces, gig and HR platforms that must verify sellers, couriers or candidates
- Public-sector and healthcare portals that need high-assurance identity
Regulatory framework: remote identification
Our team operates in Turkey, where remote identification depends on the sector. For banks, the BDDK (Banking Regulation and Supervision Agency) regulation on remote identification and establishing contractual relationships electronically is decisive; in general it foresees a video call, a check of the document’s security features and verification of chip data via NFC. Payment and e-money institutions follow the Central Bank (TCMB) rules, capital-markets firms and crypto-asset service providers follow the Capital Markets Board (SPK), and customer due diligence obligations come from MASAK (the Turkish FIU) legislation.
If you serve customers elsewhere, the local rules in your country apply as well: for example eIDAS and the EU AML framework (AMLD/AMLR and EBA guidelines on remote onboarding) in the EU, the Money Laundering Regulations and JMLSG guidance in the UK, FinCEN CIP rules in the US, or central-bank KYC rules in the GCC. Which steps are mandatory, who performs the video call, how long records are retained and which transaction limits apply differ by licence and product, so we design the flow together with your compliance officer and legal advisers.
Modules and scope
| Module | What it does |
|---|---|
| MRZ and document reading | Camera-based MRZ/CAN capture, document type detection, visual checks of security features |
| NFC chip reading | BAC/PACE secure channel, reading of data groups and the facial image |
| Chip verification | Passive and active/chip authentication against CSCA and Document Signer certificates |
| Liveness detection | Passive or active liveness to resist photos, screens, masks and replays |
| Face matching | 1:1 comparison of the selfie with the chip photo, with configurable thresholds |
| Video call | Agent-assisted video identification where regulation or risk level requires it |
| Risk scoring | Device, location, sanctions/PEP and behaviour signals combined into a decision |
| Compliance dashboard | Case review, manual approval, four-eyes principle, audit trail and reports |
| API and SDK | iOS/Android SDKs, web fallback and REST APIs for your core systems |
Technical features
- Native iOS (Core NFC) and Android SDKs, plus React Native and Flutter wrappers
- Server-side verification so that the decision never depends on the client alone
- Encrypted transport and storage, configurable data retention and deletion
- Webhooks and REST APIs for core banking, CRM and AML screening systems
- Multi-document support: national ID cards, biometric passports and residence permits that carry ICAO-compliant chips
User experience: the details that drive completion
Most drop-offs happen at the NFC step, not at the camera step. Users do not know where the antenna sits on their phone, they move the card too early, or a thick phone case blocks the signal. Clear animations that show the antenna position for the detected device model, haptic feedback, a progress indicator during the read and a friendly retry message reduce abandonment considerably. We also design a fallback path for phones without NFC or with NFC switched off, such as a video-call route or a branch visit, so that no customer is simply rejected.
Delivery models
| Model | When it fits |
|---|---|
| SDK and API integration | You already have an app and want to add NFC verification to it |
| End-to-end onboarding | We design and build the full remote onboarding journey, front end and back end |
| Cloud service (SaaS) | Fast start with a hosted verification service and usage-based scope |
| On-premise installation | Data must stay in your own data centre for regulatory or policy reasons |
| Managed service | We operate, monitor and update the platform, including certificate lists |
| Additional team | Our mobile, backend or QA engineers join your team under your direction |
Implementation steps and typical timelines
| Step | Content | Typical duration |
|---|---|---|
| 1. Requirements and regulatory review | Licence type, mandatory steps, limits, retention rules | 1–2 weeks |
| 2. Flow design | Screens, fallbacks, risk rules, manual review | 1–2 weeks |
| 3. Mobile integration | SDK integration, NFC UX, device testing | 2–4 weeks |
| 4. Server-side verification and dashboard | Certificate handling, decision engine, case management | 2–4 weeks |
| 5. Integrations | Core banking, CRM, sanctions/PEP screening | 2–3 weeks |
| 6. Testing | Device matrix, penetration test, presentation-attack tests | 2–3 weeks |
| 7. Phased rollout | Pilot group, monitoring, tuning thresholds | 2–4 weeks |
Durations are indicative and depend on scope and on how quickly decisions are made on your side. A dedicated team can typically start within 1–2 weeks.
SLA and KPI examples
| Indicator | What it shows |
|---|---|
| Flow completion rate | Share of users who start and finish onboarding |
| NFC read success | Share of successful chip reads on the first or second attempt |
| Average completion time | Minutes from first screen to decision |
| Manual review rate | Share of cases that fall to the compliance team |
| False accept / false reject rate | Quality of liveness and face-matching thresholds |
| API availability | Uptime of verification services against the agreed SLA |
| Certificate freshness | Age of the CSCA masterlist and revocation lists in use |
Target values are agreed per project; we do not promise fixed figures before measuring your user base and device mix.
What drives the cost
| Factor | Why it matters |
|---|---|
| Verification volume | Monthly checks influence licensing and infrastructure |
| Hosting | SaaS, private cloud or on-premise |
| Flow scope | NFC only, or full onboarding with video call and risk scoring |
| Platforms | iOS, Android, web and cross-platform frameworks |
| Number of integrations | Core banking, CRM, screening and e-signature systems |
| Support level | Business hours or 24/7 monitoring and incident response |
In-house team, freelancers or outsourcing
| Criterion | In-house | Freelancer | 360 Soft team |
|---|---|---|---|
| ICAO 9303 and cryptography know-how | Must be built up | Varies by person | Brought into the project |
| Regulation-ready flow | Needs compliance support | Rarely covered | Designed with your compliance team |
| Device compatibility | Needs a device lab | Limited | Device matrix testing |
| Continuity | Depends on retention | Risky | Replacement process for staff |
| Cost structure | Fixed salaries | Hourly, unpredictable | Agreed scope or monthly team |
Risks and mitigation
| Risk | Mitigation |
|---|---|
| Users struggle with NFC reading | Device-specific guidance, animations, retries and a fallback route |
| Phones without NFC or with NFC disabled | Detection, instructions to enable NFC, video-call alternative |
| Cloned or altered chips | Passive plus active/chip authentication, server-side checks |
| Presentation attacks (screens, masks, deepfakes) | Certified liveness, injection-attack detection, video-call escalation |
| Client-side manipulation | Server-side verification, app attestation, root/jailbreak detection |
| Biometric data leakage | Encryption, data minimisation, short retention, strict access control |
| Outdated certificate lists | Automated updates of masterlists and revocation lists with monitoring |
Security, data protection, NDA and IP
Identity documents and biometric data are special categories of personal data. We work under a B2B service agreement with an NDA and full IP assignment of project deliverables to you. For EU/UK clients we sign a GDPR Data Processing Agreement with Standard Contractual Clauses (or the UK IDTA where applicable); as a Turkish company we also comply with KVKK, the Turkish data protection law. Access to production data is role-based, logged and limited to what the project needs; test environments use synthetic data wherever possible.
Selection checklist
- Does the vendor verify chip signatures on the server, not only on the device?
- Are both passive and active/chip authentication supported?
- How are CSCA masterlists and revocation lists kept current?
- Is the liveness component tested against presentation and injection attacks?
- Is there a fallback for users without NFC?
- Can the flow be configured per licence, product and risk level?
- Where are biometric data stored, and for how long?
- Who owns the source code and the deliverables?
Illustrative scenario: remote sign-up in a mobile app
Illustrative scenario – not a client case.
Situation
A payment app requires customers to visit a partner location to verify their identity. Many sign-ups are abandoned between download and first transaction.
Designed solution
NFC chip reading, passive and chip authentication, liveness and face matching are added to the app. Low-risk customers are approved automatically within the regulatory limits; higher-risk cases go to video identification and manual review. Users without NFC are routed to a video call.
Results to be measured in the project
- Completion rate from download to verified account
- NFC first-attempt success by device model
- Share of cases needing manual review
- Average time to decision
Frequently asked questions
Can NFC verification be integrated into our existing app?
Yes. We provide native iOS and Android SDKs and REST APIs, so the NFC step can be added to your current onboarding flow without rebuilding the app.
Which phones are supported?
Most current Android phones with NFC and iPhones from the iPhone 7 onwards running a recent iOS version can read ICAO-compliant chips. We test against a device matrix agreed with you and provide a fallback for phones without NFC.
Can passports be read as well as ID cards?
Yes. Biometric passports and chip-based ID cards and residence permits that follow ICAO 9303 can be read with the same flow.
What is ICAO 9303?
ICAO 9303 is the International Civil Aviation Organization standard for machine-readable travel documents. It defines the MRZ, the chip data structure and the security mechanisms used to protect and verify chip data.
What is the difference between passive and active authentication?
Passive authentication proves that the chip data was signed by the issuing state and has not been changed. Active or chip authentication proves that the chip itself is genuine and not a copy, by answering a cryptographic challenge.
Why does NFC reading sometimes fail?
Typical causes are moving the card too early, holding it away from the phone antenna, thick or metal phone cases and NFC being switched off. Good on-screen guidance and retries solve most of these cases.
Is a video call still required?
It depends on the sector, licence and local regulation. Some frameworks require a video call for remote identification, others allow fully automated flows within limits. We configure the flow with your compliance team.
Where is biometric data stored?
Wherever your policy and regulation require: in your own data centre, in a private cloud or in an agreed hosted region. Retention periods and deletion rules are configurable.
How do you protect against deepfakes?
We combine chip-photo matching with liveness detection, injection-attack detection and device integrity checks, and route suspicious cases to manual or video review.
How long does an implementation take?
A focused SDK integration can be live in a few weeks; a full end-to-end onboarding with integrations and testing usually takes a few months. The team can typically start within 1–2 weeks.
Talk to us about NFC identity verification
Tell us about your licence, your target markets and your current onboarding flow, and we will propose a scope and a team. Call or WhatsApp +90 850 335 10 87, write to info@360-soft.com, message us on WhatsApp or use our contact page. Related: KYC/AML compliance software · Crypto platform compliance software · Staff augmentation in Turkey · IT outsourcing services · Türkçe