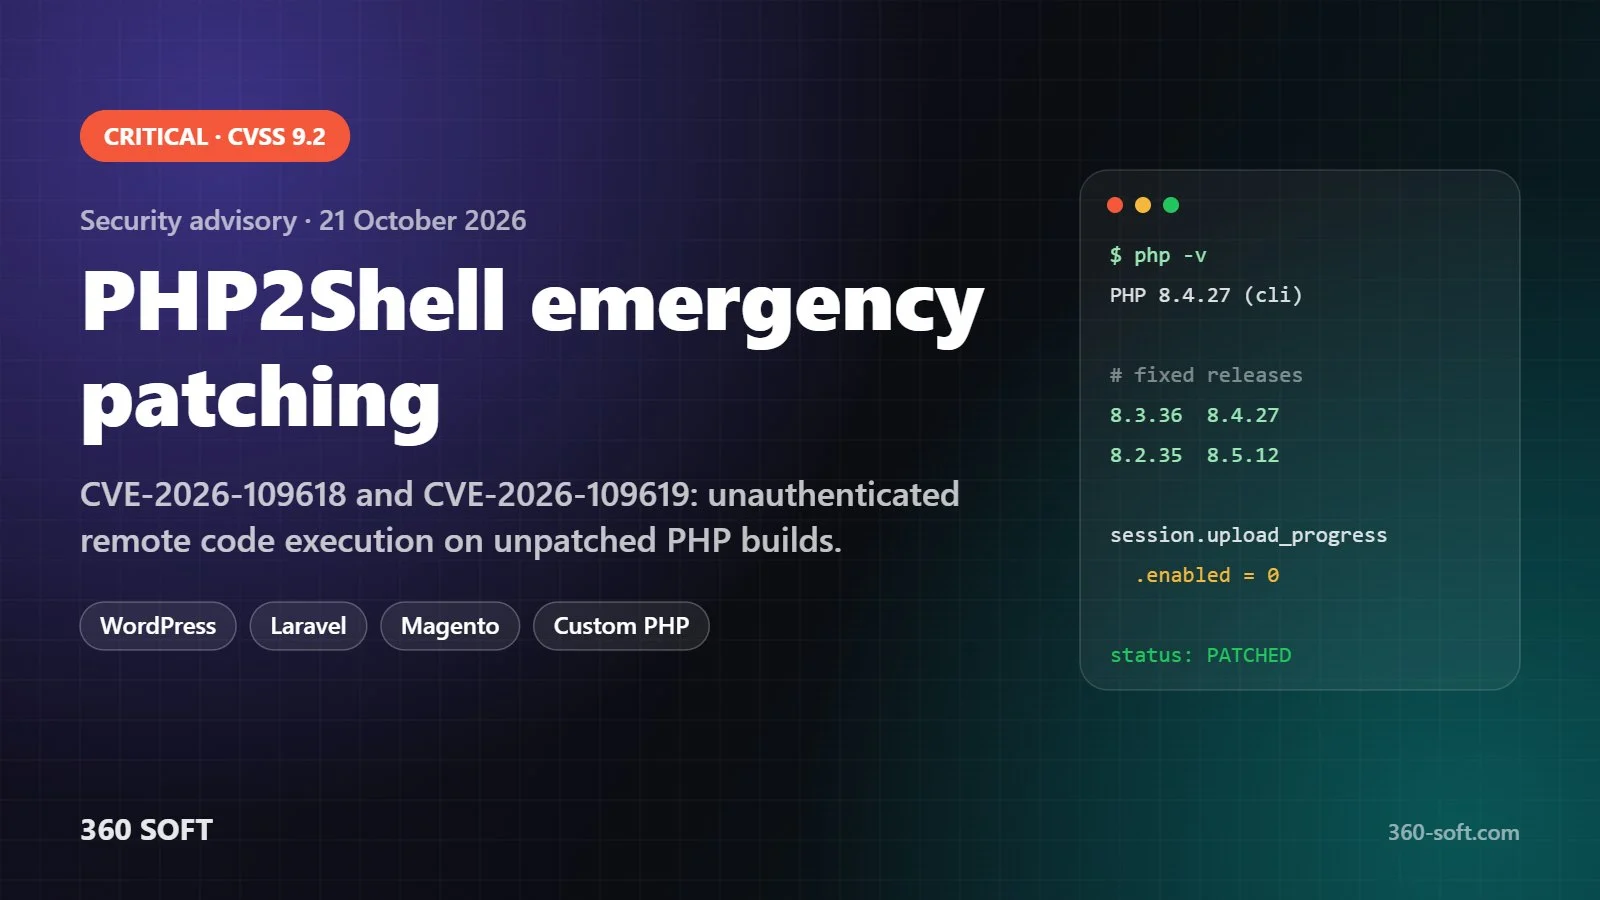
Short answer: PHP2Shell (CVE-2026-109618 and CVE-2026-109619) lets an attacker run code on servers with an unpatched PHP build, without logging in. PHP released fixed versions on 21 October 2026 and researchers have reported early exploitation attempts. Our Istanbul team finds every affected PHP system you own, applies the patch or an interim mitigation, checks for signs of compromise and upgrades end-of-life PHP versions, for clients in Türkiye, the Gulf, the UK and the EU.
Affected and fixed versions
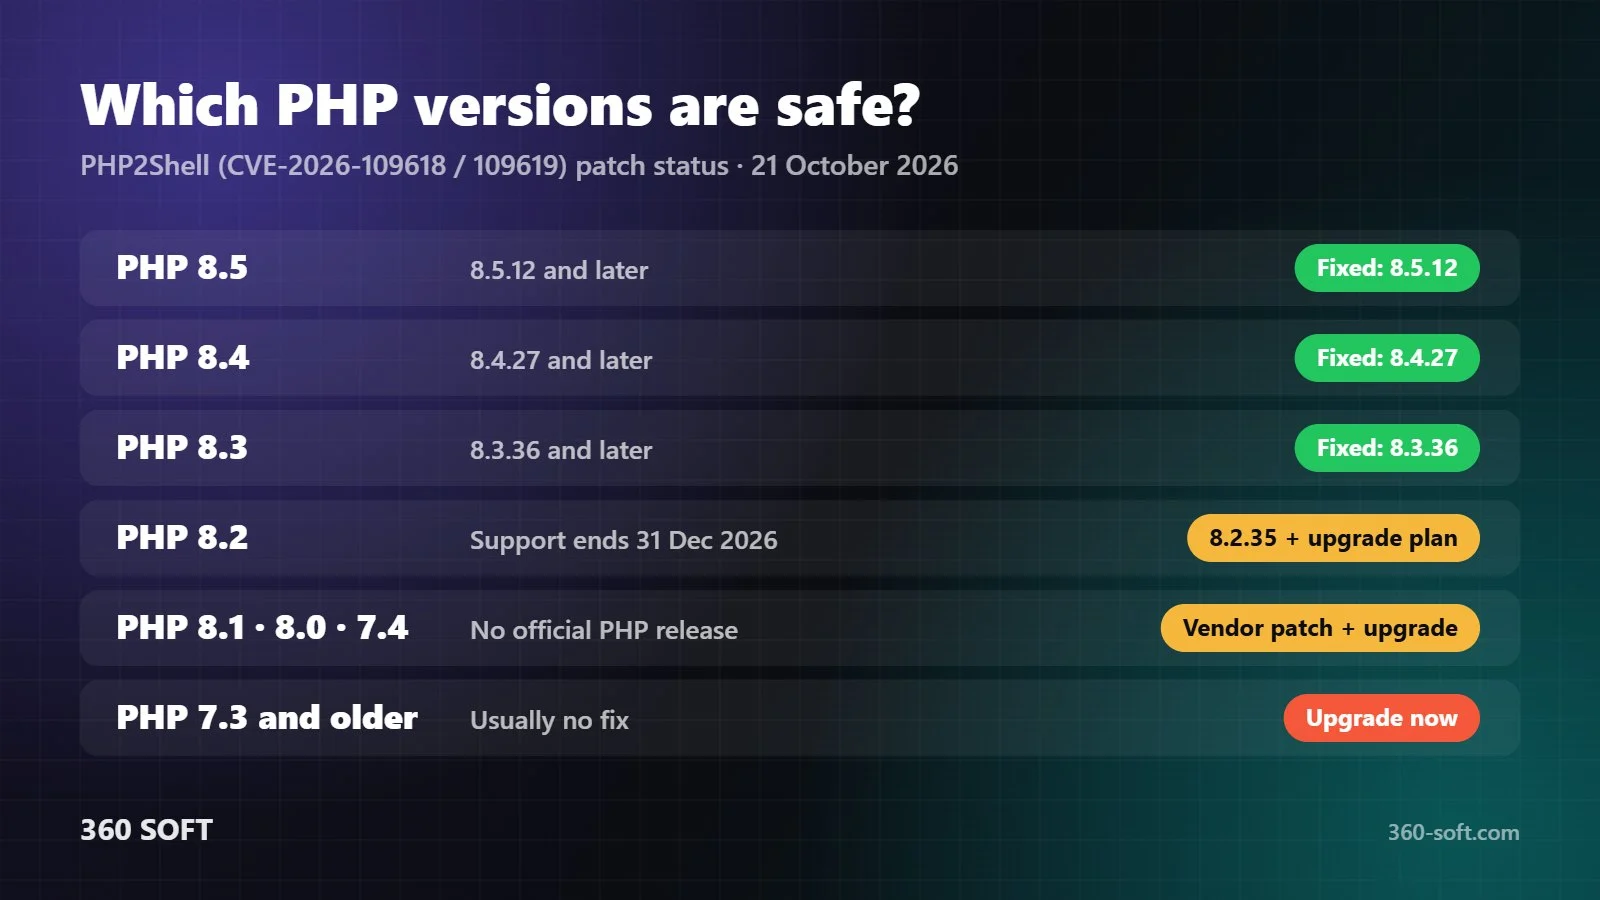
| Branch | Status | Action |
|---|---|---|
| PHP 8.5 | Affected before 8.5.12 | Update to 8.5.12 |
| PHP 8.4 | Affected before 8.4.27 | Update to 8.4.27 |
| PHP 8.3 | Affected before 8.3.36 | Update to 8.3.36 |
| PHP 8.2 | Affected before 8.2.35 | Update to 8.2.35, plan 8.3 / 8.4 (8.2 support ends 31 Dec 2026) |
| PHP 8.1, 8.0, 7.4 | Affected, no official PHP release | Vendor backport + upgrade to 8.3 / 8.4 |
| PHP 7.3 and older | Affected, usually no fix | Interim mitigation + urgent upgrade or re-platforming |
What we do
- Emergency patching: version discovery, backup, patch or interim mitigation (session.upload_progress.enabled=0, memory limit hardening, WAF rules), worker restart and a verification report.
- Estate-wide audit: inventory of all domains, subdomains and servers, risk ranking, log and file-integrity review, credential rotation plan and an executive summary for your board or auditors.
- PHP upgrades: moving WordPress, Laravel, CodeIgniter, Magento and custom PHP from 7.x / 8.0 / 8.1 to 8.3 or 8.4, tested in staging first.
- Re-platforming: rebuilding legacy PHP systems that cannot be patched on ASP.NET Core, modern Laravel or Node.js, with URLs and SEO preserved.
Why work with us
We are a software company in Istanbul, one to two hours ahead of Central European Time and one hour behind the UAE. Contracts are in English, an NDA is signed before the first call and all access is time-limited and logged. Source code, designs and accounts remain yours.
Frequently asked questions
What is PHP2Shell?
PHP2Shell is the name given to two critical vulnerabilities in the PHP interpreter, CVE-2026-109618 and CVE-2026-109619. The PHP security team rated both 9.2 on CVSS v4.0. They can allow unauthenticated remote code execution on unpatched servers.
Is my site affected if my application code is secure?
Yes. The flaws are in PHP itself, not in your application. WordPress, Laravel, Magento, Drupal, Joomla and custom PHP applications are all exposed if they run on an unpatched PHP build.
Which PHP versions are fixed?
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, released on 21 October 2026. There is no official PHP release for 8.1, 8.0 or 7.4; fixes for those come from vendors such as cPanel and CloudLinux. Versions 7.3 and older have no fix in most environments.
How fast can you respond?
We start the assessment on the same day. For a single server, patching or interim mitigation is usually completed within 24 hours. Larger estates start with an inventory and are handled in risk order.
Request emergency help
Tell us your domain, the platform you run (WordPress, Laravel, custom PHP, Magento) and your hosting type (shared, VPS, own servers). Requests outside office hours are forwarded to the team.
We have received your request.
We will e-mail you a written quote with scope, timeline and price within 24 hours.
Sources: PHP security advisory (21 October 2026), Tenable, Wiz and CERT-EU notes. Updated 22 October 2026.